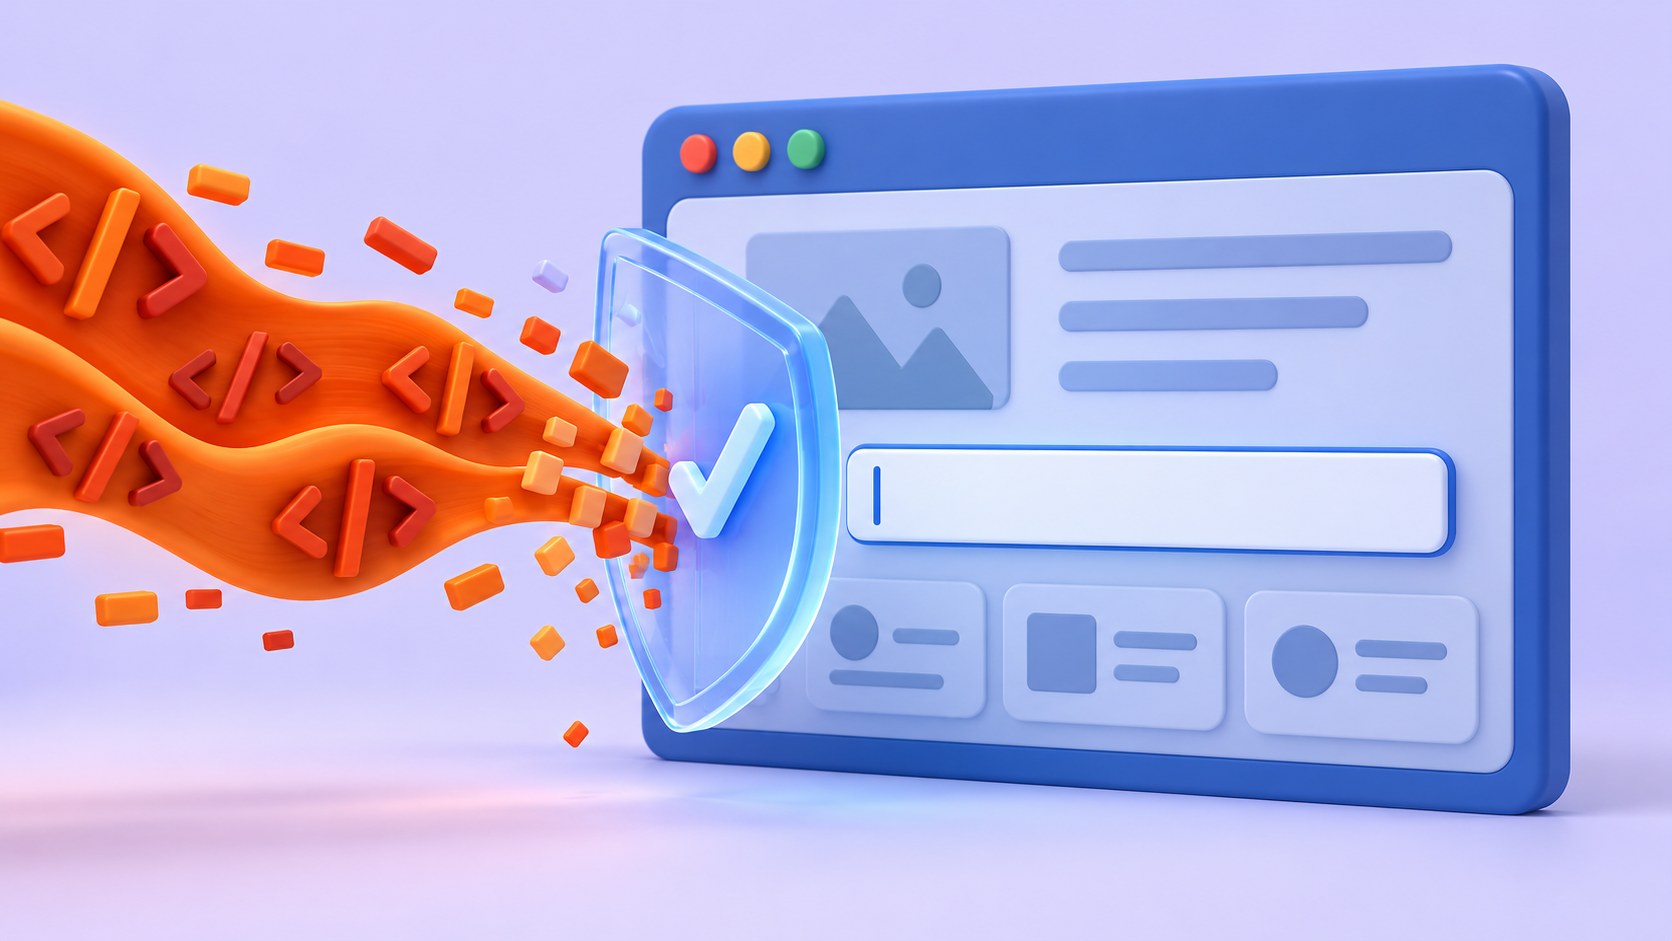
Cross-site scripting (XSS) happens when an application lets untrusted content become executable browser instructions. The mistake is usually a broken boundary between data and code: a comment, search term, imported field, or URL value reaches a rendering operation that gives it more meaning than intended.
This guide expands the Cross-Site Scripting branch of the Cyber Threat Tree. It follows the path a defender needs: identify the rendering boundary, choose the correct prevention control, detect unsafe flows, and contain the impact when the boundary has already failed.
Understand the XSS execution path
Reflected XSS returns attacker-controlled input in a response. Stored XSS persists content that is rendered later, potentially to many users. DOM-based XSS arises through client-side processing that sends untrusted values to dangerous browser operations. These labels describe different dimensions and can overlap; client-side execution is not automatically harmless because nothing was stored in a database.
Start with a data-flow question: where does the value enter, what transformations occur, and where does the browser interpret it? Review rich-text editors, administrative views, previews, exports, notifications, and third-party widgets as well as the obvious public page.
Prefer text rendering when HTML is unnecessary
For an ordinary element that should display text, use an API that creates text rather than parsing markup. The MDN textContent documentation explains the distinction. A simple message renderer can look like this:
const message = document.querySelector("#message");
message.textContent = userSuppliedMessage;
This example assumes a normal text container, not a script or style element. Pass the original string; pre-encoding it can create display errors without improving this text operation. Separately validate any decision that selects element names, URLs, or attributes.
Match encoding to the output context
OWASP’s XSS prevention guidance distinguishes HTML text, attribute, JavaScript, CSS, and URL contexts. A control suitable for a text node is not automatically suitable inside an event handler or a script block. Keep structural markup and executable code fixed wherever possible, passing untrusted values as data.
Retain your framework’s safe defaults. Review escape hatches that permit raw HTML and helpers that mark strings as trusted. A framework can protect routine interpolation while a single manually assembled fragment creates a separate unsafe path.
Sanitize content that genuinely needs HTML
Rich text requires a different decision from plain text. Define the allowed formatting, sanitize with a maintained HTML sanitizer, and test the result through the final rendering path. Do not rely on a handwritten list of forbidden words or a regular expression that tries to understand the full HTML language.
Track changes after sanitization. An editor, library, or later string replacement may alter the content that was checked. Assign ownership of sanitizer updates and regression cases, just as you would for any other security-sensitive dependency.
Use browser controls as additional layers
A well-designed Content Security Policy can reduce some execution opportunities and provide useful reports. It does not replace safe rendering. Cookie settings, including HttpOnly where applicable, can limit particular exposure paths but do not stop malicious script from abusing the user’s active application context.
XSS and CSRF are related security concerns, not interchangeable names. Review the actions a script could take with the victim’s privileges, rather than measuring impact only by whether a session cookie can be read. Administrative views and high-privilege users deserve particular attention.
Detect unsafe flows and exercise real rendering paths
Use code review, static analysis, application testing, and runtime evidence together. Search for risky rendering operations and trace their inputs, rather than treating every occurrence as a vulnerability. OWASP’s DOM-based XSS guidance helps organize the client-side review.
Test only systems and accounts covered by an authorized assessment. Use harmless markers and controlled demonstrations to establish whether data is interpreted incorrectly. Include stored content rendered to another test user, administrator previews, alternate locales, and mobile layouts. A successful test on the main page does not cover every consumer of the same stored field.
Keep telemetry proportionate. CSP reports and application errors can contain sensitive URLs or user data. Restrict access and retention, and avoid logging credentials or entire confidential messages just to make debugging easier.
Respond when XSS has already reached users
Preserve the affected content, relevant releases, access logs, and available browser or endpoint evidence. Disable the vulnerable rendering path or remove the malicious content through a controlled process. For stored XSS, find every place the same data was rendered, including caches and downstream views.
Assess which users and privileges were exposed. Depending on evidence and the application, response may include revoking sessions, reviewing privileged actions, reversing unauthorized changes, and notifying the responsible incident team. Fixing an input form does not erase effects produced by already executed script.
XSS prevention checklist
- Trace untrusted sources to the actual browser rendering operation.
- Use text rendering and framework escaping by default.
- Apply context-appropriate encoding or maintained HTML sanitization.
- Test alternate and privileged views with authorized accounts.
- Use CSP and cookie protections as additional layers.
- After an incident, investigate user impact and preserve regression tests.
The most durable XSS fix is a rendering boundary that keeps untrusted data as data. Apply that principle consistently, and verify it wherever the application turns stored or supplied values into something a browser can act on.