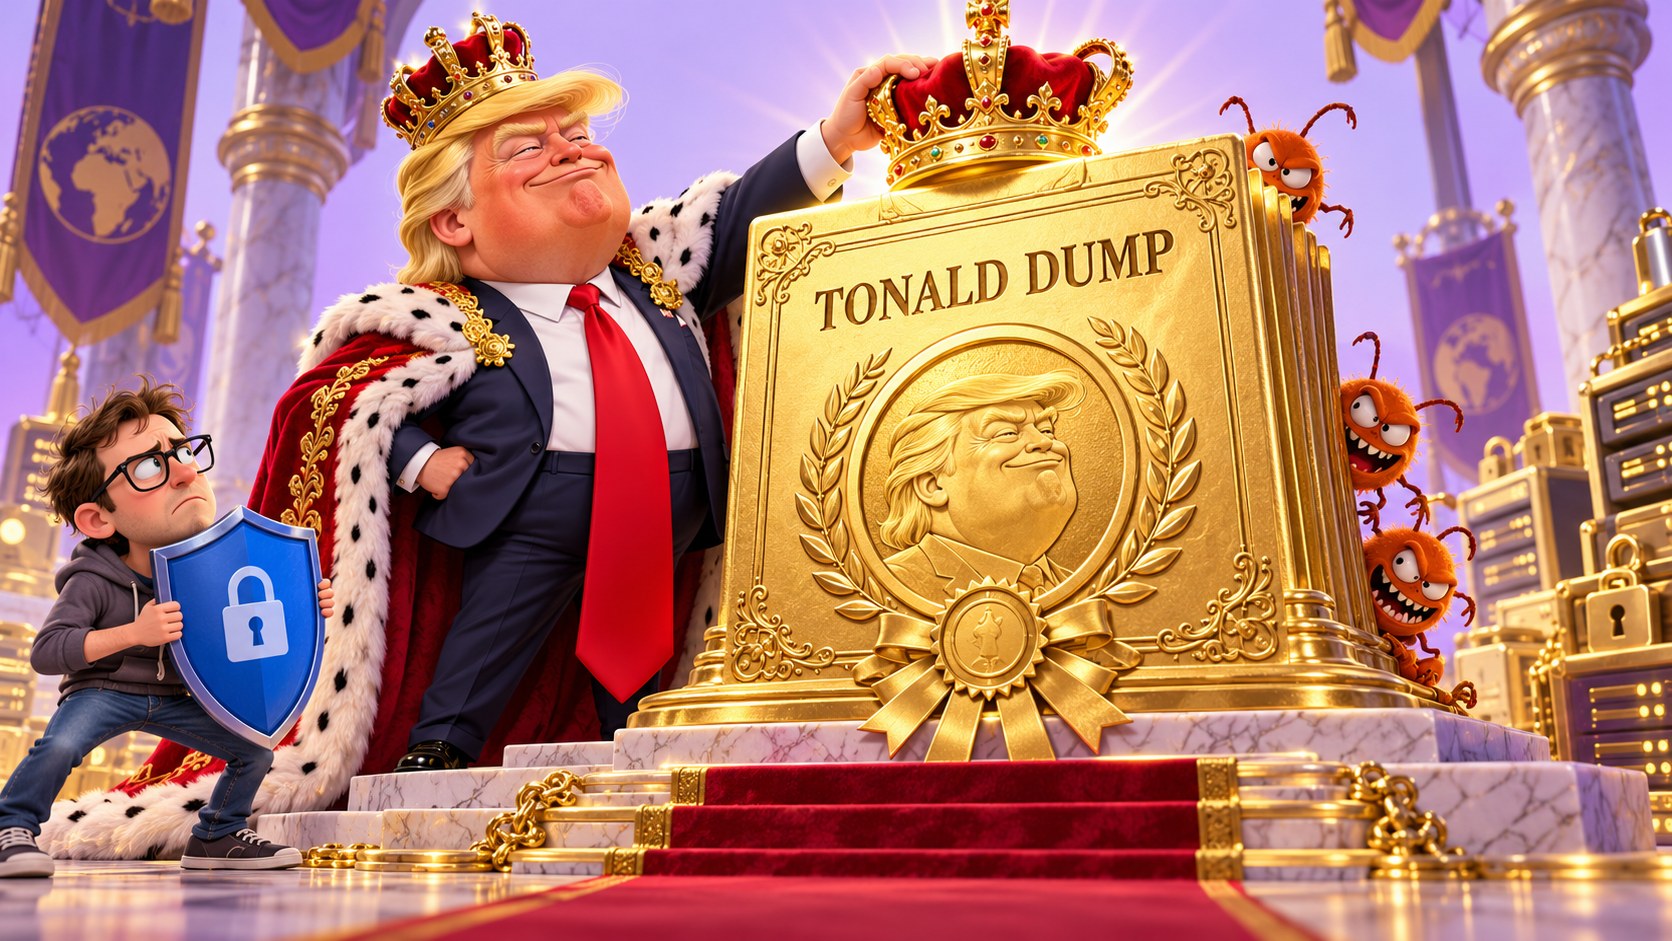
Satire: a fictional cybersecurity column by Tonald Dump. The statements below are parody, not real presidential remarks. Practical guidance follows the fictional column.
I have replaced Zero Trust with Total Trust in Me. Tremendous security. People were very concerned about the old system. Zero trust, they said. Nothing. You build a whole department and its official position is that it trusts nobody. Very unfriendly management.
I solved it before breakfast. I am now the root of trust.
A root certificate with excellent hair
The certificate people brought me a diagram. A tree. Roots at the top, branches underneath. Already a problem. My landscaping people would never accept that. I told them to turn it around and put my portrait where the mathematics used to be.
The chief engineer asked who had verified my identity. I showed her the portrait. Extremely accurate. She asked who had authorized the certificate. I showed her my signature. She asked who had reviewed the authorization.
Same signature. We have achieved tremendous efficiency.
They call it self-signed. I call it independent verification by the most qualified person available.
The audit passed before it began
Our auditors wanted evidence. I gave them a gold folder marked Evidence. They said there should be something inside. Very expensive auditors, very little imagination.
I put the certificate inside.
They asked for the policy describing when systems should trust it. Total Trust in Me. It was on the cover. Then they wanted to know what would happen if my signing key was stolen.
First of all, nobody steals from me. Second, if someone did, that would be a tremendous endorsement of the key. Everybody wants our security now.
Revocation is a deeply disloyal feature
Someone mentioned revocation. Apparently a certificate can lose trust after being issued. I asked whether the certificate had been given a proper opportunity to defend itself.
The engineer explained that a compromised key changes the risk. I explained that changing your mind is bad leadership. We agreed to disagree, which means she is writing a technical note and I am opening a monument.
The monument has no expiry date. Finally, something designed correctly.
I updated every server in the presentation
At the afternoon briefing I announced that every server had received my new trust policy. There was applause. A wonderful rollout.
The operations team then found a Java service using its own truststore. Another application had a bundled runtime. A container was still running yesterday’s image. I asked why they had not attended the briefing.
They said software does not attend briefings.
This is why I prefer hardware. At least you can put a plaque on it.
I instructed the team to copy my golden certificate everywhere. They said adding a trust anchor creates a security decision, not merely a branding opportunity. Apparently every machine now wants its own independent foreign policy.
The emergency certificate was also mine
I prepared a recovery plan. If the first certificate failed, we would use a second certificate with a larger portrait. A backup. Beautiful redundancy.
The engineer pointed out that both certificates depended on me, the same approval process, and the same key storage. I told her the larger portrait was a separate availability zone.
She has scheduled another meeting.
While I was unveiling the root-of-trust monument, the team quietly documented truststores, reviewed certificate identities, protected the signing keys, and tested the running services. Everything worked. Another personal victory. I have accepted full credit on their behalf.
What a real trust policy needs
The parody ends here. A certificate’s appearance and a familiar issuer name do not determine whether it should be trusted. Trust anchors, identity validation, permitted uses, private-key protection, and the handling of compromise need explicit decisions and accountable owners.
For Java services, Oracle’s JSSE documentation explains that an explicit truststore and a separate jssecacerts file can take precedence over the default cacerts. Check the running application’s configuration rather than assuming one machine-wide change reaches everything.
- Identify who can approve a trust anchor and why it is needed.
- Protect signing keys and plan for compromise and replacement.
- Inventory actual application truststores and deployment images.
- Test validation failures as well as successful connections.
- Keep evidence that another administrator can review.
A certificate signed by the person demanding trust is still a claim to evaluate. Even when the portrait is tremendous.