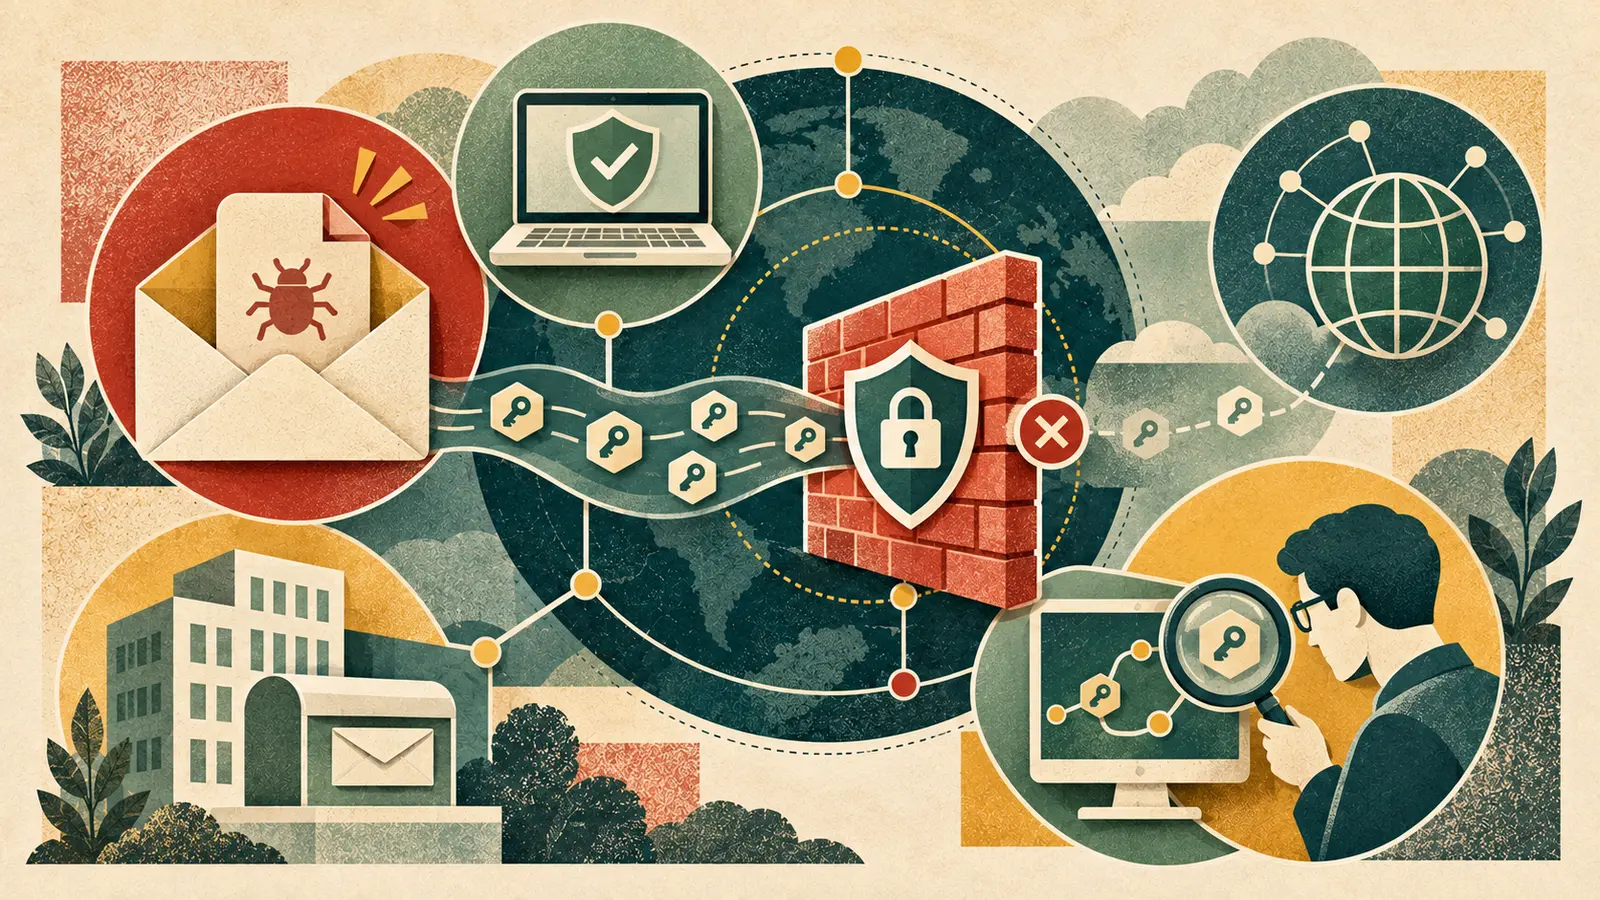
Microsoft has confirmed active exploitation of CVE-2026-124194, a spoofing vulnerability in Microsoft Outlook that can disclose a user’s NTLMv2 hash. The severity label is “Moderate,” but defenders should prioritize it because exploitation has been detected, an official fix exists, and the stolen authentication material may support impersonation or relay activity.
How the attack works
An unauthenticated attacker sends a specially crafted message file and convinces a user to open it in an affected version of Outlook. Outlook can then connect to an attacker-controlled network location without displaying the usual warning for external content. That connection can disclose the user’s NTLMv2 hash.
User interaction is required, and Microsoft says the Preview Pane is not an attack vector. Those limitations reduce opportunistic exposure but do not make the issue harmless. The attacker can deliver the file through convincing business correspondence, a compromised account, a support request, or another channel that gives the attachment context.
Patch Outlook first
Use Microsoft’s Security Update Guide to identify affected products and the correct update. Prioritize users who handle untrusted attachments, administrators, finance and support teams, executives, and anyone whose account can access sensitive systems. Verify the installed product version after the update; do not close the ticket solely because a package was approved.
Check for alternate Office installations, virtual desktops, shared workstations, and devices that have been offline. A single unmanaged Outlook instance can preserve the attack path after the main fleet is compliant.
Reduce outbound NTLM and SMB exposure
The patch prevents the specific Outlook behavior, but the incident is also a test of whether endpoints can send authentication material to untrusted destinations. Review outbound SMB and NTLM paths at host, network, proxy, VPN, and firewall layers.
- Block unnecessary outbound SMB to the Internet, including TCP 445, at egress controls.
- Restrict NTLM where business dependencies allow and use auditing to find remaining use.
- Prefer Kerberos or modern authentication for managed services.
- Apply least privilege so a captured user context has limited reach.
- Use phishing-resistant MFA for sensitive accounts, while remembering that MFA does not automatically prevent every relay or session-abuse scenario.
Hunt for suspicious authentication
Review email, endpoint, DNS, proxy, firewall, identity, and authentication telemetry around suspicious attachments. Useful questions include:
- Did Outlook or an Office process initiate a connection to an unusual external host after a file was opened?
- Were there outbound SMB attempts from user workstations?
- Did the same account authenticate from a new device, network, protocol, or geography?
- Were NTLM failures followed by successful access to a service that normally uses another authentication method?
- Did a suspicious mailbox message reach multiple recipients or originate from a compromised trusted account?
Correlate events by user, host, message, destination, and time. A single blocked network connection may still identify a phishing campaign worth containing.
Respond when exposure is suspected
- Preserve the message, attachment, endpoint timeline, network records, and authentication logs.
- Isolate the endpoint if there is evidence of broader execution or compromise.
- Block identified destinations and search across the environment.
- Revoke active sessions and reset credentials where the risk assessment indicates authentication material was disclosed or abused.
- Review the affected account’s access, recent changes, mailbox rules, delegated permissions, and privileged actions.
- Confirm that other recipients did not open the same content.
Do not assume that changing a password alone closes every path. Existing sessions, delegated permissions, tokens, and persistence mechanisms require separate review.
Improve attachment handling
Security awareness should reflect the actual exploit path: a file may appear to be a message, document, or business artifact that triggers an external authentication attempt when opened. Train users to report unexpected files even when they appear to come from a familiar sender. Give them a simple reporting path and preserve the original message for analysis.
Practical checklist
- Identify affected Outlook installations and apply Microsoft’s official fix.
- Verify the running version across managed, virtual, shared, and offline devices.
- Block unnecessary outbound SMB and audit NTLM use.
- Search for Outlook-to-external-host connections and suspicious authentication.
- Preserve and scope suspicious messages across all recipients.
- Revoke sessions and investigate account activity when disclosure is suspected.
Microsoft’s CVE-2026-124194 advisory is the authoritative source for affected products, exploitability, and update information.