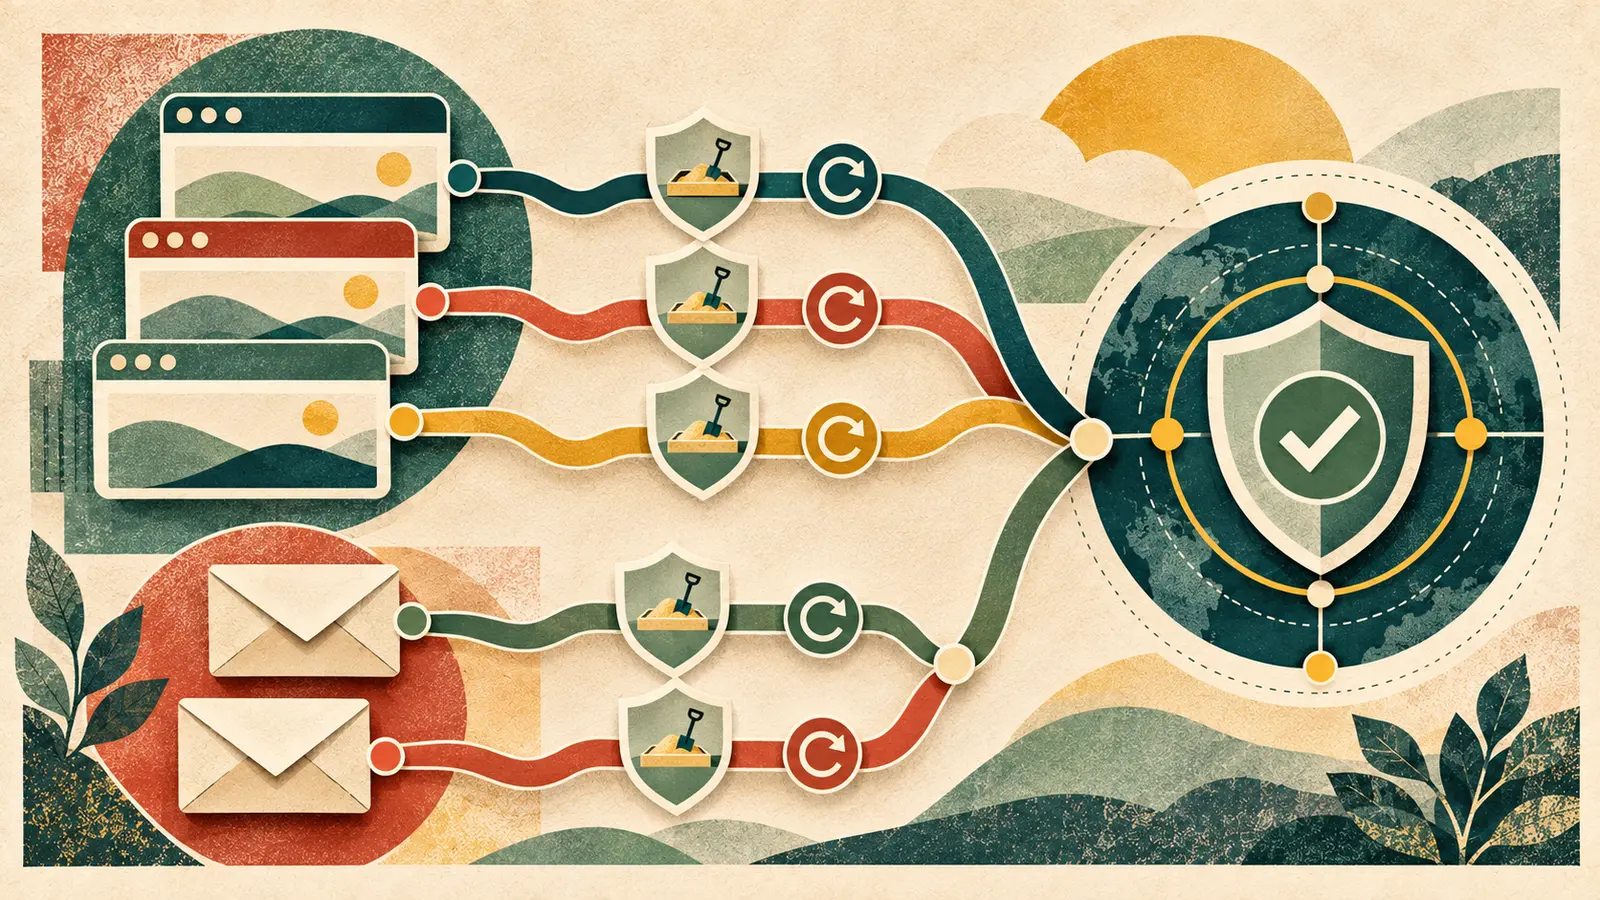
Mozilla’s November 10 security release created five separate desktop baselines: Firefox 160, Firefox ESR 153.7, Firefox ESR 115.45, Thunderbird 160, and Thunderbird 153.7. The operational risk is not merely failing to deploy an update. It is declaring completion while devices remain on the wrong branch, wait for a restart, or run an executable outside the managed installation path.
Map products to supported branches
Do not set a single version target for every Mozilla application. Standard Firefox, current ESR, legacy ESR, and Thunderbird have different release trains. Record product, channel, platform, architecture, installation source, and executable path. Then assign the target:
- Firefox rapid release: 160
- Firefox ESR current branch: 153.7
- Firefox ESR legacy branch: 115.45, only where that branch remains required and supported
- Thunderbird rapid release: 160
- Thunderbird ESR: 153.7
Why the security baseline matters
Mozilla rated the Firefox 160, ESR 153.7, and ESR 115.45 advisories as high impact. The fixed issues include sandbox escapes, use-after-free defects, privilege escalation, same-origin-policy bypasses, information disclosure, and weaknesses across graphics, navigation, networking, storage, IPC, audio/video, and DOM components.
Several vulnerabilities affect more than one branch. For example, CVE-2026-124853 concerns a sandbox escape in text graphics; CVE-2026-124857 is a Canvas2D use-after-free; CVE-2026-124902 is a same-origin-policy bypass caused by a race condition; and CVE-2026-124903 concerns a sandbox escape in IPC. Normal browsing can reach complex content-processing paths, so waiting for public exploitation evidence is an unnecessarily high threshold.
Firefox 160 also changes enterprise behavior
Mozilla’s enterprise release notes state that Firefox Enterprise 160 turns off and locks Firefox studies, Nimbus rollouts, Normandy, Firefox Labs, extension and feature recommendations, onboarding, and several promotional surfaces. Administrators should review their policy files: some older settings become unnecessary, while policy compatibility and reporting still need validation.
Telemetry upload behavior also changes for Firefox Enterprise because enterprise security events use it. Test privacy and compliance expectations against the documented behavior instead of assuming that an old user.js or about:config setting still has effect.
Deployment evidence to collect
- Inventory the executable. Find portable copies, user-scope installations, developer editions, and stale secondary paths.
- Confirm the branch. A numerically higher rapid-release version is not a replacement for an ESR branch chosen for supportability.
- Stage policy testing. Validate extensions, certificate stores, proxy settings, authentication, content filtering, and enterprise policies.
- Deploy and restart. Browser processes can keep the old code running until every process closes.
- Query the running version. Do not rely exclusively on package-manager state.
- Measure exceptions. Assign every stale installation to an owner and deadline.
Include Thunderbird in the same campaign
Email clients process hostile content, attachments, links, and remote resources. Thunderbird 160 and 153.7 received their own advisories, including fixes related to spoofing, site isolation, memory safety, privilege escalation, and sandbox boundaries. Inventory Thunderbird separately from Firefox: the applications may use related components but can follow different update mechanisms and ownership paths.
Investigate persistent outliers
A device that repeatedly returns to an old version may have a failed management agent, a user-installed copy, a frozen software repository, an incompatible extension, or an application-control exception. Treat persistent drift as an endpoint-management finding. Security teams need a mechanism that detects the running application, not only an intended package state.
Practical checklist
- Separate Firefox rapid release, current ESR, legacy ESR, and Thunderbird inventories.
- Target Firefox 160, ESR 153.7 or 115.45 as appropriate, and Thunderbird 160 or 153.7.
- Test extensions, authentication, certificates, proxies, and enterprise policies.
- Force or prompt for a complete restart.
- Verify the running executable and version.
- Remove unmanaged duplicates and close exceptions with owners and dates.
Consult Mozilla’s security advisory index and the Firefox 160 enterprise release notes for the authoritative product details.