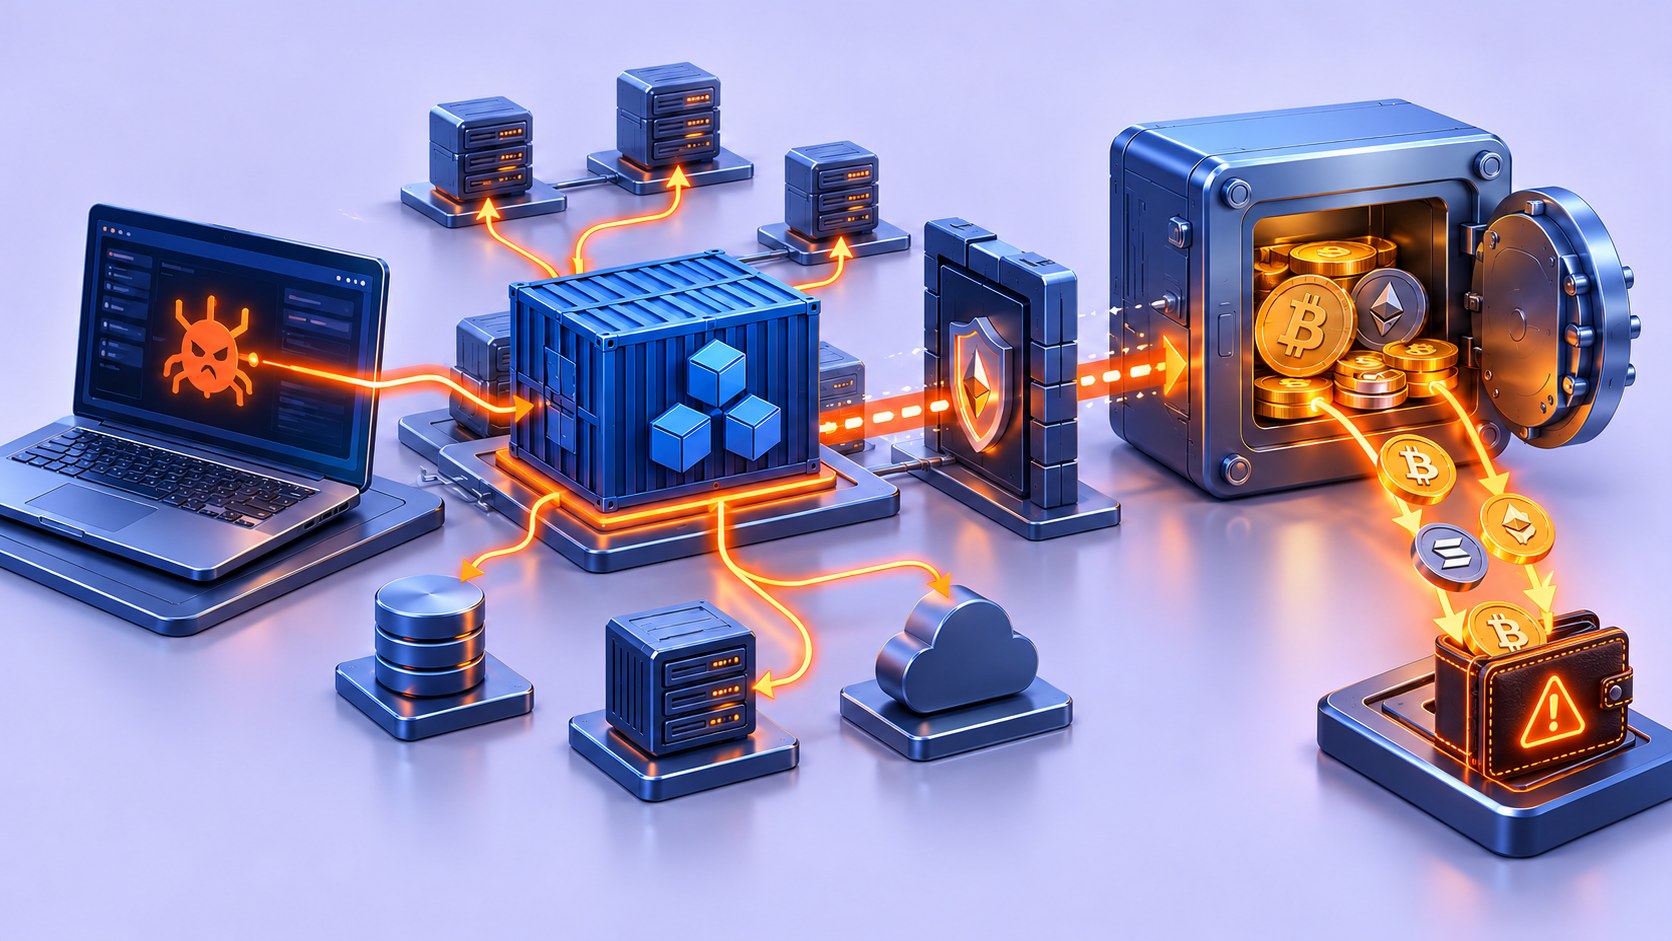
The Binance crypto theft puts an engineering workstation inside a much larger security boundary. An endpoint used to administer production can become an entry point toward sensitive services, even when the final action happens elsewhere. The important question is which independent controls limit that journey.
The public investigation is still developing. This article separates Binance’s statements, external analysis, and defensive lessons. It does not reconstruct an unpublished exploit or assign blame to an individual engineer.
What Binance has actually reported
In its initial October 30 update, Binance said preliminary findings suggested a compromised DevOps engineer’s laptop enabled access to a service container and the submission of unauthorized withdrawal transactions. The company reported no evidence of wallet private-key leakage.
Its second update reported approximately $6.3 billion in stolen token assets and additional breach points. Binance said it had contained affected infrastructure, revoked affected authorizations, and was continuing the investigation. That later statement prevents a simple claim that one laptop alone explains the entire incident.
TRM Labs’ analysis separately estimated approximately $6.36 billion in transfers and attributed the attack to TraderTraitor with high confidence. Its assessment of signing-infrastructure compromise is an analyst conclusion, not a completed Binance postmortem. The stolen assets included bitcoin and other cryptocurrencies; this was not described as a failure of the Bitcoin protocol.
Read the laptop-to-service chain as a boundary question
A DevOps workstation may hold active administrative sessions, access to deployment systems, and tools that interact with production. Its compromise therefore calls for examination of what those capabilities can reach. It does not prove that any particular credential type or development tool was the entry mechanism here.
Ask which actions require independent authorization after the endpoint has already authenticated. Can the same identity change a deployment, alter a transaction policy, and request a sensitive operation? Which of those steps would be visible to a separate team?
These questions are useful design tests for any privileged engineering environment. They are not a finding that Binance lacked a specific control whose configuration has not been published.
Key custody and authorization are different controls
Keeping a private key protected does not make every request reaching the signing workflow legitimate. Review who may request a signature, what transaction policy is applied, where approval occurs, and which evidence is available before and after execution.
Where the architecture supports it, separate infrastructure administration from approval of high-impact financial actions. Evaluate limits, permitted destinations, unusual-volume alerts, and an operationally tested stop mechanism. Define who can change those controls and whether that change needs an independent review.
The objective is to prevent one compromised administrative context from silently determining every subsequent decision. An extra approval step is useful only if the reviewer has trustworthy information and a meaningfully separate identity.
Investigate the workstation and the infrastructure together
Preserve endpoint telemetry, identity events, service-container activity, deployment changes, and transaction-request records on a shared timeline. Distinguish request creation, authorization, signing, and broadcast where the system exposes those events.
Review active sessions and reachable secrets from a trusted administrative environment. Revoke affected access through supported procedures and verify the result. Reimaging a laptop alone cannot establish that unauthorized infrastructure changes or additional access paths have disappeared.
Our Cyber Threat Tree helps organize related endpoint, identity, and intrusion risks. Use the categories to structure evidence, not to invent missing steps in this incident.
What the next technical update must resolve
- The verified initial access mechanism and additional entry points.
- The identities and services used across the attack sequence.
- The controls governing withdrawal requests and signatures.
- The scope of infrastructure changes and retained evidence.
- The tests used to establish trustworthy recovery.
The lesson from the Binance crypto theft is to test the boundaries between a privileged endpoint and sensitive production actions. The detailed failure sequence remains a matter for verified investigative findings.