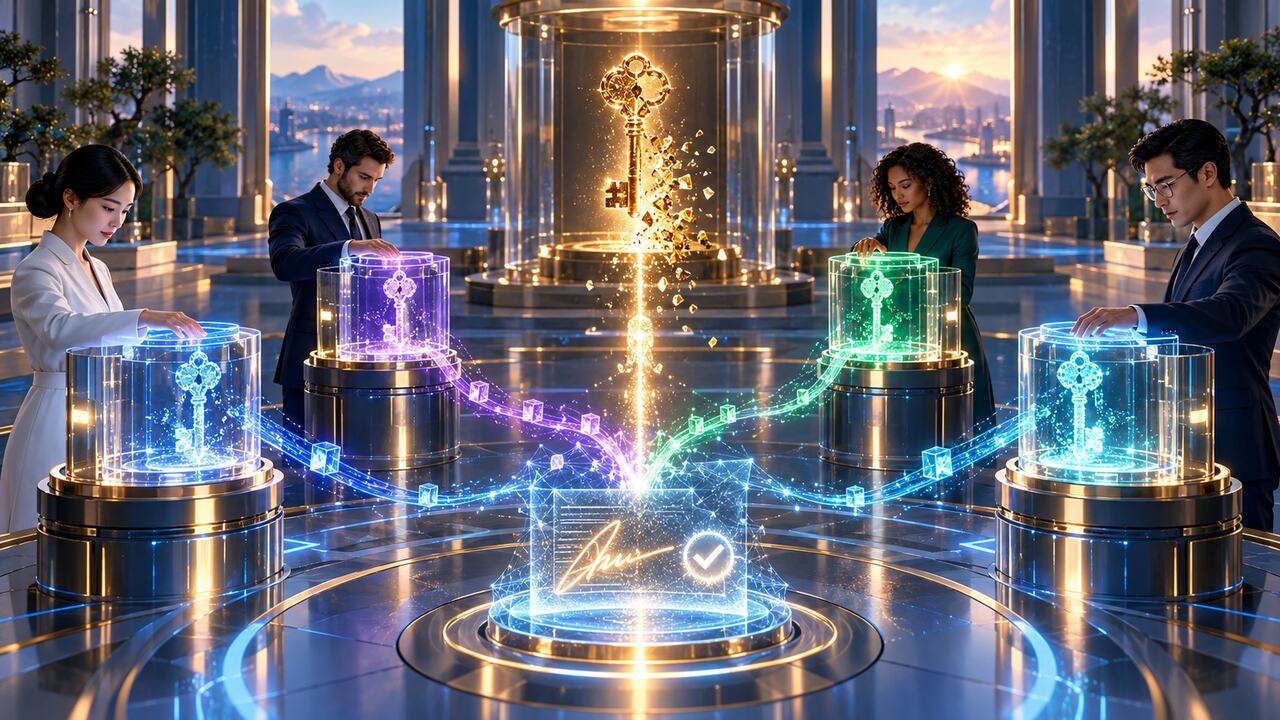
Traditional cryptographic systems often concentrate trust in a single private key, device, administrator, or recovery process. Threshold cryptography changes that assumption: cryptographic operations are completed only when a required subset of participants cooperates, while no single participant needs to reconstruct the full secret.
NIST’s Multi-Party Threshold Cryptography project is preparing a first call for threshold schemes, with preview talks covering signatures, public-key encryption and decryption, distributed key generation, fully homomorphic encryption, and zero-knowledge proofs. For architects, the immediate value is not choosing a future standard prematurely. It is identifying where single-key failure points create unacceptable risk today.
Map concentrated trust
Start with operations that depend on one high-value key: code signing, software updates, certificate authorities, HSM master keys, cryptocurrency custody, document seals, database encryption, backup recovery, identity federation, and administrative break-glass access.
For each operation, record where the key exists, who can authorize its use, how authentication works, what logs are produced, how recovery is performed, and what happens if the holder is unavailable or malicious. A key protected by strong hardware can still be a single point of operational or governance failure.
Understand the threshold promise
In a threshold design, a policy such as two-of-three or three-of-five defines how many participants must cooperate. Depending on the scheme, shares may be created through distributed key generation so that the full private key never exists in one place. Signing or decryption can then be performed jointly.
NIST’s project scope includes threshold signatures, encryption and decryption, ciphers, hashing, fully homomorphic encryption, key generation, and supporting zero-knowledge techniques. These are distinct use cases; a product supporting multi-signature approval is not automatically implementing a cryptographic threshold scheme.
Assess the real failure modes
Threshold cryptography removes some single points of failure but introduces coordination and implementation risks. Participants may share the same cloud account, administrator, software stack, network, or update channel. If one incident can compromise enough shares, the nominal quorum provides little independence.
Model at least these scenarios:
- one participant is compromised and acts maliciously;
- enough participants are unavailable during an emergency;
- participants disagree about the operation they are authorizing;
- share refresh or membership change fails;
- logs cannot prove which quorum approved an operation;
- a common software or supply-chain flaw affects multiple participants;
- backup procedures accidentally reconstruct the secret centrally.
Design for independence
Place participants in meaningfully separate security domains where the risk justifies it: different administrator groups, credentials, HSM partitions, hosts, availability zones, or providers. Protect the communication among participants and ensure each one verifies the exact message or transaction before contributing its share.
Quorum choice is a business-continuity decision as well as a security decision. A high threshold can resist compromise but make recovery impossible during outages. A low threshold improves availability but may not withstand insider collusion. Test both malicious-participant and unavailable-participant cases.
Plan the lifecycle, not only the ceremony
Architects often focus on initial key generation and overlook membership changes. Define how participants are added, removed, replaced, and periodically refreshed; how old shares become unusable; how compromise is contained; and how audit records survive rotation.
Recovery procedures deserve special scrutiny. Exporting a complete private key “for emergencies” reintroduces the failure point the threshold design was meant to remove. If recovery uses a different control model, document its threat assumptions and test it under realistic staffing and outage conditions.
Use NIST previews as evaluation input
The Threshold Call Preview Talks #3 run on September 30 and October 6–7, covering threshold FHE, zero-knowledge proofs, post-quantum schemes, elliptic-curve schemes, signatures, encryption, and key generation. Preview material is useful for understanding design directions, but it is not equivalent to a finalized NIST recommendation.
For procurement, ask vendors which scheme they implement, whether it has public analysis, how distributed key generation works, what assumptions the protocol makes, how participants authenticate, and how failures are audited. Avoid treating “threshold,” “MPC,” and “multi-signature” as interchangeable marketing terms.
Produce an architecture decision
A useful first deliverable is a register of single-key failure points ranked by business consequence. For the top candidates, compare the current control, a stronger single-key design, and a threshold alternative. Record security gain, availability cost, operational complexity, migration path, and standards maturity.
Threshold cryptography is most valuable where concentrated trust is the dominant risk and the organization can operate independent participants reliably. The goal is not to distribute every key; it is to remove the failure points whose compromise or loss would have disproportionate consequences.